
This is not a post about Thrall, please stop asking
The Out-of-Touch Adults’ Guide to Kid Culture: Looksmaxxing With Dangerous Drugs
We may earn a commission from links on this page.
This week’s column is bleak. First, there’s the looksmaxxing trend where teenagers are taking dangerous chemicals to correct perceived physical shortcomings. Then there are the AI job interviewers. Depressing, but at least some young people are having a little fun with their dystopian hellscape.
Looksmaxxing teenagers are DIY bio-hacking
You can judge a generation by the illegal drugs it pioneers. In the 1960s, hippies smoked weed and dropped acid to expand their consciousness; the yuppies of the go-go ’80s fueled their drive to acquire with Colombian cocaine; but kids today don’t want to go deeper or work harder. They have a smaller, sadder goal: They take drugs to look better. The substance of choice for a growing number of teenage boys are steroids, peptides, and other exotic chemicals designed to enhance appearance.
Would-be muscle-men have been injecting themselves with black market ‘rhoids since the Eisenhower administration, but that was a small cult of adult weirdos with a specific goal. In 2026, kids are into it, and they aren’t using steroids to win a $500 prize in the Mr. Topeka contest; they’re using unapproved research chemicals to looksmaxx. Looksmaxxing is an online movement of young men trying to maximize their physical appearance. Teenagers are taking the normal desire to look their best to dangerous, pathological levels. Driven by a combination of undiagnosed body dysmorphia and relentless social media algorithms that turn amoral “red pill” kooks into gurus, teenage boys are ingesting a panoply of exotic and dangerous compounds in a quest to fix the angle of their jawlines, change their skin tone, lose weight, grow taller, and otherwise “correct” perceived physical problems.
In the “good old days” of steroid abuse, people generally stuck to abusing anabolic-androgenic steroids that had at least been tested for decades. Teens today are buying SARMs (Selective Androgen Receptor Modulators) and synthetic peptides marked “not for human consumption” from shady laboratories online. Steroids primarily affect the muscles, but many of these newer substances target different biological systems. A recent Rolling Stone article reports that kids are “heightmaxxing” by swallowing erdafitinib, a drug that treats advanced urothelial cancer, because the drug is known to trigger growth spurts (that can result in a curvature of the spine and other nasty side effects). They’re also trying MK-677 to get taller, an experimental growth hormone secretagogue that carries the risk of insulin resistance, water retention, and high blood pressure. Others are injecting Melanotan II, a synthetic peptide that forces a long-lasting deep tan, with side effects of extreme nausea and the sudden, aggressive darkening of moles. (And they’re doing steroids too.)
For a look at how this often ends, check out the Hulu documentary Get Huge that details the death and madness that surrounded “Dr.” Tony Huge, a pioneer in the looksmaxxing world, or subscribe to Coach Kolton’s YouTube channel, where the grim consequences of extreme looksmaxxing are presented in graphic detail.
What are “softmaxxing” and “hardmaxxing?”
In the looksmaxxing community, softmaxxing is doing generally-considered-acceptable things to look better, like getting enough sleep, exercising regularly, and eating a balanced diet. Hardmaxxing is taking more extreme measures like plastic surgery, smashing your face with a hammer, or taking experimental drugs.
What does “natty” mean?
In the bodybuilding and looksmaxxing community, “natty” refers to a natural, non-steroid-enhanced physique.
What are the bicep heart and waist heart trend?
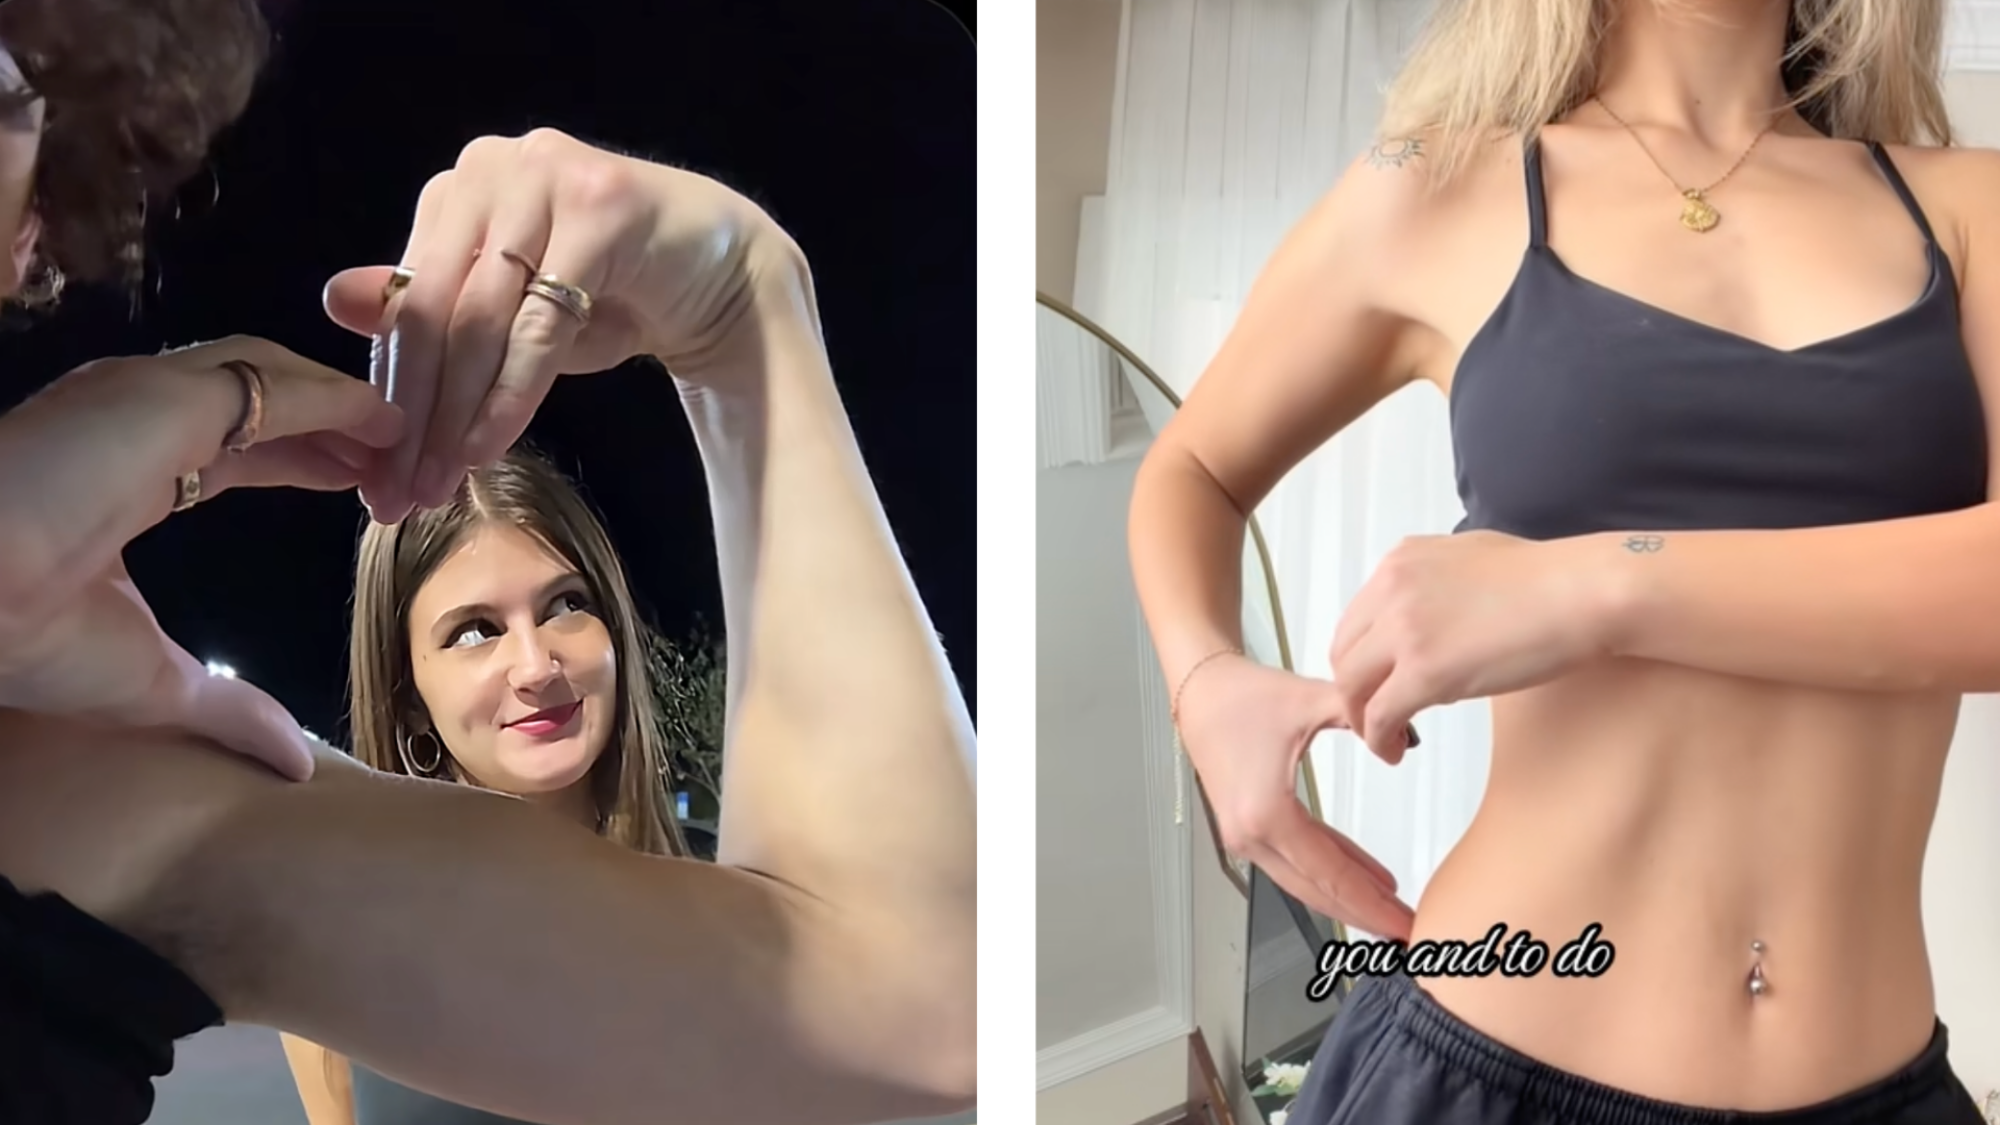
Credit: @montanaandryan, @nurciinguldiiken – TikTok
Here’s something more lighthearted than the growing popularity of illicit self-esteem chemicals: the bicep heart and waist heart trends. The Bicep heart came first. Thirst trap videos started appearing on Instagram and TikTok in October in which dudes make a heart with their hand and bicep. Then people started posting variations where they frame the shot with someone they love inside the heart. The bicep heart quickly led to women posting the waist heart.
Okay. So maybe it’s not that lighthearted of a trend. While there are some videos of dudes with skinny arms doing the bicep heart, it’s mostly jacked dudes. And the waist heart doesn’t seem like it would work at all unless you are a specific shape, as this video illustrates. So maybe this isn’t a silly meme but an illustration of how young people are inundated with content that can trigger feelings of physical unworthiness, even if they’re just looking for silly memes.
Viral videos of the week: messing with AI job interviews
As if searching for a job wasn’t alienating and horrible enough, some companies have begun using AI agents to conduct interviews. Begging a robot to let you work in a cubicle farm is as dystopian as anything Phillip K. Dick ever imagined, but don’t count humanity out yet. Young people are sticking a finger in the eye of the machine by creating comedy videos that focus on trolling these AI job interviewers. They’re hilarious because AI is the ultimate straight person in a comedy team, and the raw compute costs to run these interviews means corporate money is burning with each second of wasted time. Here are some of the top creators in the genre.
Bo Bongo: This YouTuber shows up to AI interviews shirtless but insists he’s wearing a “corporate tube top,” then focuses on daring the interviewer to notice he’s doing things like smoking a cigarette or eating a rotisserie chicken.
Cam Whitt likes to wind up AI by arguing, interrupting, telling outrageous lies, and asking the dumbest questions imaginable, like, “When does the interview actually start?” and “How do I figure out what my name is?”
Grahamn Raabe: Among this YouTuber’s schticks is speaking only in nonsense, like describing his professional background as “freight cadence, walnut, a little bit of Richard, spruce wood—six years of spruce wood.”
Nick Reid: Is so obnoxious, he seems to make the AI furious at him, even though it’s a computer without emotions. Two thumbs up!
Optimizely Hack Turns World’s Biggest Websites Into Malware Dispensers
PattonPending writes: As reported by The Register, Zoom, the BBC, CNN, HSBC, and numerous other websites briefly served malware on November 16 after an attacker exploited Optimizely’s “Experiments” feature to inject JavaScript into their pages through Optimizely’s CDN. The malware replaced cryptocurrency addresses, attempted to steal credit card information and cookies, and sought to compromise iOS devices. Websites belonging to at least 178 organizations were affected via the “OPTIMJACK” vulnerability, which has since been patched. “Earlier today, Optimizely identified a security incident in which an unauthorized party exploited a vulnerability in Experimentation and used it to add malicious JavaScript to some customer projects,” the company said. “We’ve fixed the vulnerability and removed the injected code from affected projects. We’ve also taken steps to secure affected user accounts and put additional protections in place to prevent unauthorized code from being delivered.”


The researchers said they found malicious code in 188 of the 1,611 Optimizely scripts examined, including those on the company’s own website and login portal, suggesting the number of affected businesses could be significantly higher.
Read more of this story at Slashdot.
Waymo is pausing all freeway rides after California DMV says the robotaxis are ‘imminent hazard to public safety’
Restrictions were made by California’s DMV after a driverless Waymo was caught trying to pass a Highway Patrol vehicle that was slowing traffic.
Google To Keep Temporary Gemini Chats For Two Months
timob58 shares a report from TechCrunch: Google is extending how long it keeps temporary Gemini chats and conversations made with chat history turned off to around two months, saying the change aims to improve safety and security as AI systems become more capable. The change, which will roll out globally in the Gemini app over the coming weeks, marks a significant increase from the previous 72-hour retention period mentioned in Google’s Gemini Apps Privacy Hub, according to an archived version from November 12. OpenAI, by comparison, says it may keep temporary chats in ChatGPT for up to 30 days, whereas Anthropic retains incognito chats in Claude for 30 days by default.


Google did not answer questions about what prompted the change and whether it would affect how conversations are accessed or reviewed, instead pointing to a blog post that says chats are kept longer to respond to users, process feedback, and protect its services and users. Its updated Gemini Apps Privacy Hub also cites potential system failures as a reason for retaining chats and says temporary conversations are not used to train AI models. “A recent explainer on AI and business IP notes that providers keep data for abuse monitoring even when it is not used for training,” adds timob58.
Read more of this story at Slashdot.
GIMP Adds Automated UI Testing for Linux X11 and Wayland
GIMP adds automated UI tests covering image creation, PNG exports, layers, zoom controls, and other common operations.
Yet another satellite company is jockeying for a rocket—but this one makes sense
Finnish satellite developer ICEYE announced Tuesday that it is seeking to buy Italian rocket-maker Avio for more than $2.2 billion in a transaction aimed at creating Europe’s first true vertically integrated end-to-end space company.
The announcement came as an all-cash voluntary tender offer from an Italian subsidiary of ICEYE to Avio’s shareholders, led by the Italian defense conglomerate Leonardo. Avio said its board of directors “has taken note of the notice” from ICEYE and is considering the purchase offer.
Avio builds the Vega C rocket, a solid-fueled launcher designed to carry up to 3.3 metric tons (7,300 pounds) of payload to low-Earth orbit. The Vega C has flown successfully seven times in eight attempts since 2022. It is a follow-on to an earlier version of the Vega rocket that amassed a 20-for-22 record since debuting in 2012.
Hundreds of websites deliver potent malware cocktail to unsuspecting visitors
Hundreds of websites using the Optimizely website personalization platform served unsuspecting visitors a potent malware cocktail that targeted cryptocurrency wallets, stole payment card data, cookies, and screenshots, and delivered exploit kits for infecting iPhones and iPads, researchers said Tuesday.
ReportURI said it identified 178 websites—including CNN, Zoom, the BBC, and Salesforce—that were affected. JavaScript digitally signed by Optimizely and then loaded into customer pages had been modified to include malicious components that attempted to infect visitor devices with multiple payloads. When wares were installed successfully, they swapped user cryptocurrency wallet addresses for the attackers. Other components skimmed payment cards, stole cookies and screenshots, and, on iPhones and iPads, delivered iOS exploit kits known as Coruna and DarkSword.
Optimizely infrastructure delivers multipurpose malware
Optimizely serves JavaScript “snippets” that include both company code and code that is provided by each customer. The JavaScript, which can be served directly from Optimizely or from a customer endpoint, runs on every page the customer serves. Somehow, the attackers wrote their own code into a portion of each affected customer’s JavaScript and then delivered it from cdn.optimizely.com. A valid certificate for that domain signed the JavaScript.
NVIDIA’s board chair says the company is not considering reinstating Jensen Huang as CEO
NVIDIA’s board chair said it doesn’t want Jensen Huang back in the CEO role during the company’s first earnings call since his resignation.
There’s a chance your Xbox Series X is plugged into the wrong HDMI port
Make sure you’re getting the most out of your Xbox Series X, starting with a port check.
Nvidia Stopped Disclosing Singapore Sales As Revenues Hit $104 Billion
Nvidia stopped separately disclosing its Singapore sales (source paywalled; alternative source) after changing its geographic revenue reporting methodology from customer billing addresses to headquarters locations, obscuring a business that generated $104 billion in external revenue in 2025, up 72% from the previous year. The Financial Times reports that the change has drawn scrutiny amid U.S. investigations into whether Singapore-based Megaspeed helped smuggle Nvidia chips into China. From the report: “There is now a lot more focus on Nvidia’s Singapore business and questions about who its end customers are,” said an investor who is investigating Nvidia’s dealings in south-east Asia. The Singapore accounts show that the subsidiary booked $117.8 billion of revenue in the 12 months to January 2026, including $13.6 billion of sales to another Nvidia company. Given the nature of the Singapore operation as a global hub, customers it serves are from all over the world. Only a small quantity of the chips Nvidia sells ends up in or goes through Singapore. The Singapore subsidiary generated just $53 million of profit in the year to January 2026, suggesting limited scope for Nvidia to benefit from Singapore’s low corporate tax rates.


[…] Singapore’s outsized role as a revenue generator for Nvidia used to show up in the company’s overall results. In January 2025, the US company reported that Singapore was its second-biggest geographic area by revenue, based on customer billing location. The Singapore office generated $23.7 billion of revenue, behind only the US and representing 18 per cent of global income, based on customers’ billing location. The annual accounts said that most of the business was generated by customers using the Singapore office to centralize invoicing and that most of the products were shipped elsewhere, with less than 2 per cent of revenue tied to chips that landed in the city-state.
As recently as July last year, Nvidia reported that the Singapore office accounted for 22 per cent of total revenue. This was around the time Nvidia said it began cutting ties with Megaspeed, following US Department of Commerce investigations into the business. Nvidia then changed its financial reporting methodology and stopped splitting out revenue that went to the Singapore office. Before the 2025 reporting change, Nvidia said in its financial filing that it booked sales based on the billing locations of its customers, but that the end customer’s location “may be different than our customer’s billing location.” It added that “most shipments associated with Singapore revenue were to locations other than Singapore and shipments to Singapore were insignificant,” according to the filings.
Read more of this story at Slashdot.
RIP To ‘We Got X Before GTA 6’ Memes
I mean, I guess you can keep saying it, if you want
Two Independent Projects Want to Bring MATE to Wayland, Each in its Own Way
Polo builds a new compositor for MATE, while MATE Wayland Desktop runs MATE on labwc from an Ubuntu-based ISO.
Intel Benchmarks Show 350W GPU D270 Beating NVIDIA’s RTX PRO 6000 By 5.9×
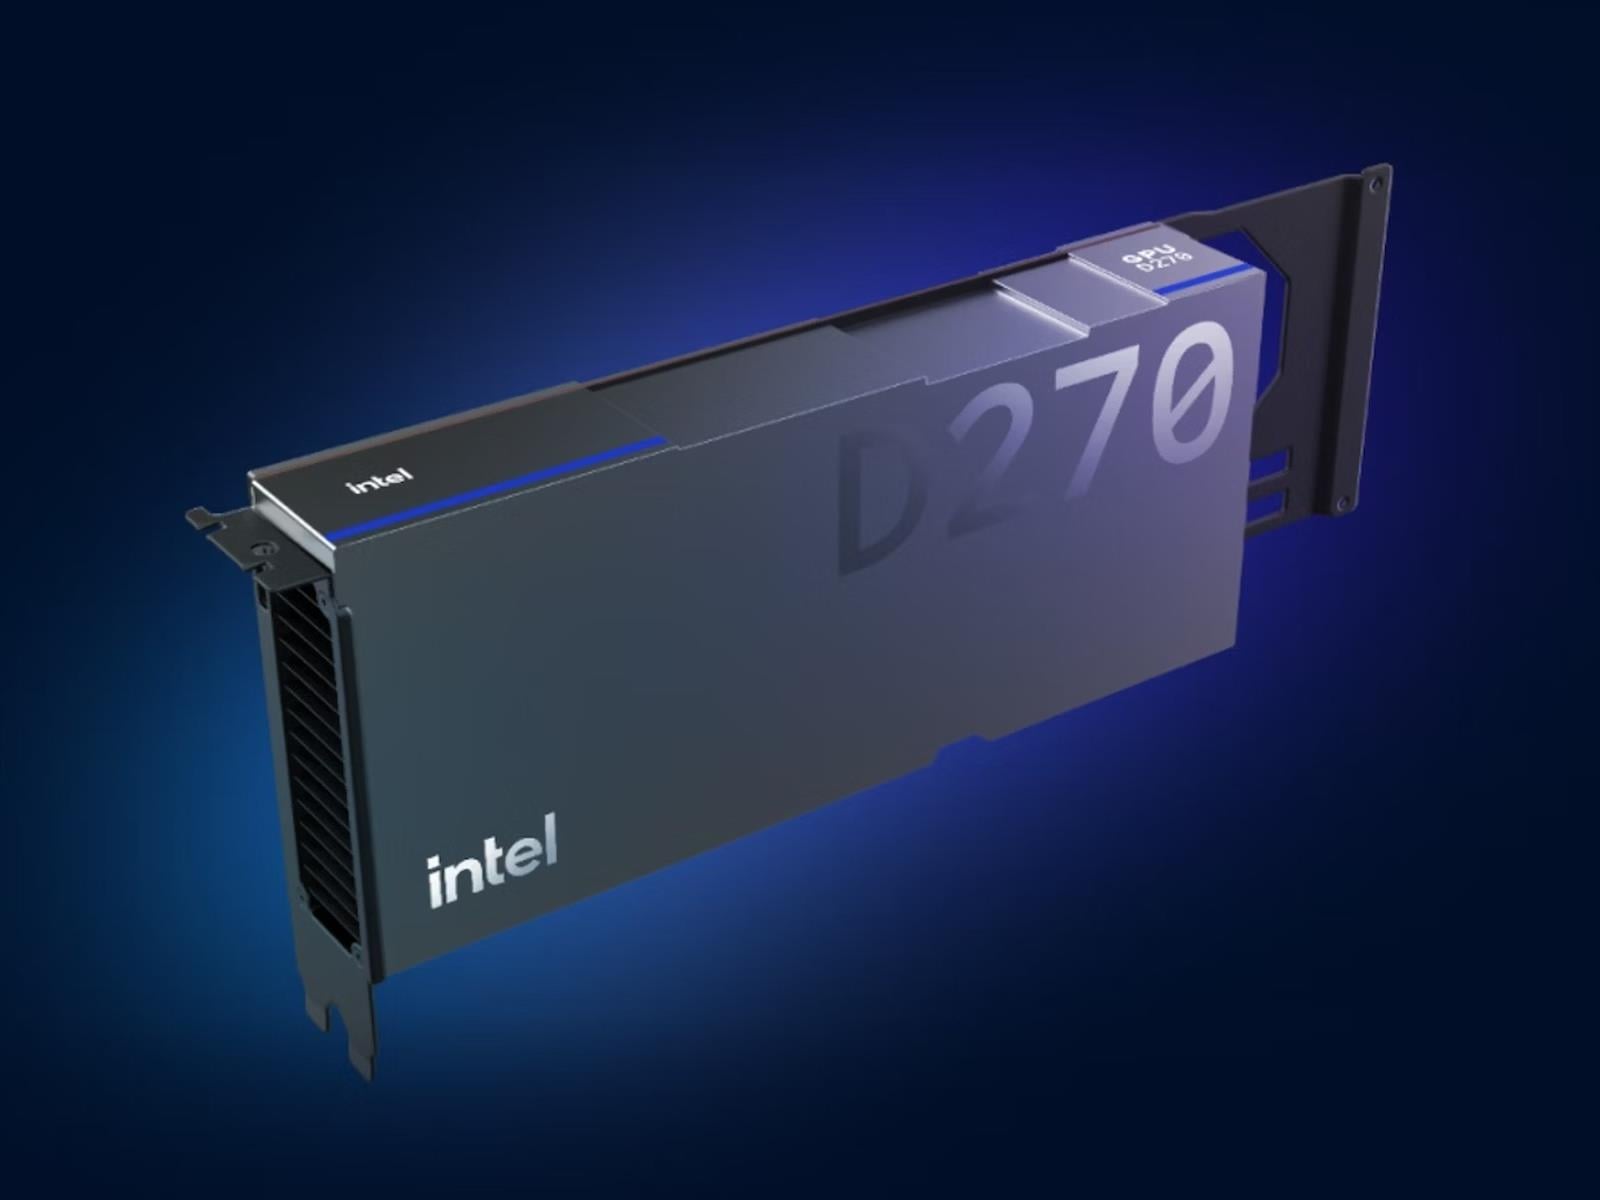
Intel’s latest “GPU” product, the non-graphics-capable GPU D270, is an extremely powerful compute accelerator. How powerful? Well, it only has 32 Xe3P cores, nominally the same number as the Arc Pro B70. However, according to Intel, it can beat
Java4Shell Vulnerability For OpenJDK Java That Can Lead To Remote Code Execution
Java4Shell was publicly disclosed this afternoon as the latest high profile security vulnerability in the age of AI and LLMs…
Why Do AI Posters All Look Like That?
You know “the look” by now. Every poster for a business or event has pictures of uncanny-looking people, buildings that don’t look right, and always that one font. But why? If generative AI is supposedly able to “think” and be “creative,” why do so many of its results come out looking exactly the same? The answer is complicated, and it has to do with what chatbots define as “thinking.”
At this point, gone are the days of chatbots like ChatGPT, Claude, or Gemini simply generating text immediately in response to a prompt. Some very fast models do, but most employ what’s known as “thinking models”, which are a bit of a misnomer. The “thinking” really just consists of generating a set of sub-prompts before executing the main one. And it’s in that hidden, generated text that most of the “choices” (to the extent that we can call the statistical output of an AI model a “choice”) occur that determine how a design looks.
The hidden “design brief” behind every AI poster
To borrow a classic and implausible example, if you were to give an AI chatbot the instruction “Make a peanut butter and jelly sandwich,” it would start by generating step-by-step instructions on how to make the sandwich before trying to make one (if it could). Most of this happens invisibly in the background, and many proprietary chatbots won’t show you their in-process “thinking” prompts even if you ask.
In the case of an AI poster, it might break down “make a poster” into smaller steps such as “create a design brief for a poster.” To demonstrate this while doing some testing for this piece, I added additional prompts for ChatGPT to explain the “design briefs” it generated, which included details like layout, colors, and typography.
The problem is those instructions are still subject to the same flaws as any other AI-generated text. They can’t properly fact-check; they can’t walk into the real world and see the thing they’re describing; and they can hallucinate or fall back on stale formats that become easy to notice after a while.
For example, while testing, I had ChatGPT generate a poster for a Lifehacker-themed nightclub. In every case, the underlying brief it generated outlined some basic details, but occasionally it added things I hadn’t asked for. This included additional text, iconography, and in one case it even added the “design brief” explanation I had requested as the bottom half of the poster.
Those mistakes filter into the final product, when the brief is then fed into the image generator that ultimately makes the poster. In my case, ChatGPT showed me the underlying explanations for its reasoning (though even that could be different from what was actually sent to the image generator), but most people who use a chatbot for this task won’t see these factors before getting the final result.
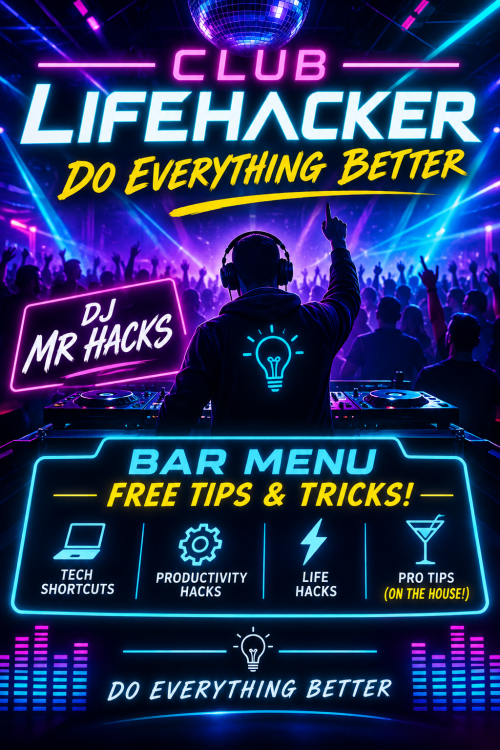
Credit: Eric Ravenscraft/Lifehacker
“Choices” are still driven by statistical models
While most chatbots won’t show you exactly what underlying “thinking” they use, most can be coaxed into describing the vague outlines of how they reached certain outcomes. And those descriptions provide some insight into why certain chatbots keep outputting similar results over and over. It doesn’t take long for some patterns to emerge. For example, any prompt to generate a poster for a nightclub almost invariably generated a brief that had specifications for a color palette including “electric purple,” “electric yellow,” and “electric pink.”
The reason for this should be pretty obvious: When the statistical model underlying LLMs needs to come up with an example for “colors for a nightclub poster,” the most obvious answers are neon, high-energy colors. Unless you know something about the specific club’s vibe (and write that out and feed it to the chatbot), the AI will have to fill in the gaps with something. And that something will be based on the same statistics it uses to predict any word.
This pattern of repetition was everywhere in all the design rationale ChatGPT gave me. Across multiple attempts to generate a Club Lifehacker poster, the generated design brief added an overarching “concept” that described the fictional club’s atmosphere as “high-energy” and “futuristic.” Every bot mentioned using images with the “silhouette” of either the DJ or a dancing crowd (often both). All the text had to be “bold” and “futuristic.”
That one font “choice” might be a misinterpretation
If there’s one dead giveaway that a poster was made with AI, it’s that one brush-stroke font that they all seem to use. Now, this is a bit more speculative, but I have a theory on where that specific design comes from. And it’s worth noting upfront that this seems to only apply to posters generated by ChatGPT specifically.
One of the most common factors I found in my design brief testing was the use of phrases like “brush lettering” or “brush script.” Brush lettering is a design term that refers to using any number of methods like markers, paint brushes, or brush pens to write text. In digital design, that can take the form of fonts that are designed to emulate the look of fancy, handwritten text.
In every test poster I created, however, ChatGPT seemed to take the phrase “brush lettering” rather literally. Every instance I encountered of a design brief that mentioned any kind of “brush” text generated an image with letters that looked as though they were created with a broad paint brush. A human designer would understand “brush lettering” to mean “something that looks handwritten,” but ChatGPT didn’t seem capable of understanding the phrase as anything other than using an actual paint brush.
The generated posters aren’t even using a “font,” strictly speaking. (Often, letters that should be identical had slight variations.) The image generator part of the chatbot is still a diffusion model, so it can’t employ a vector-based font, per se. But the brush-style font is so common that its look surfaces in any statistical model.
This is an odd quirk of ChatGPT specifically, and it’s possible that it could change in the future. Especially if OpenAI intentionally tries to train this behavior out of its chatbot. However, it’s helpful to illustrate the underlying mechanism. The only way a chatbot can conceptualize design elements in a visual medium is to generate more specific text to feed to the image generator. And that text is just as prone to mistakes and blandness as any other AI model.
Every chatbot has a “house style” (even if it’s an accident)
I’ve been examining this with a focus on the kinds of posters ChatGPT generates because they’re very common, but posters (or any AI-generated content) from other models might look different. Every model has its own tendencies. For example, a lot of vibecoded websites are made with Anthropic’s Claude, and you can often tell by the tiny text, buttons with rounded corners, and tile-based layouts.
To a certain extent, this is inevitable. While AI models are very different from humans and do not make “choices” in the same way people do, design elements still have to come from somewhere, and whether human or AI, it’s impossible to make these decisions in a vacuum. Humans will have preferences based on the things they like or emotionally resonate with, and AI models will have tendencies based on what their statistical model determines is the most appropriate output.
That means that an AI model’s “style” is naturally going to change over time. Even if a model improves or makes fewer mistakes, it’s impossible to ever change the fact that all ChatGPT images are made by ChatGPT. Whatever you generate with any particular model will have a lot in common with what everyone else who uses the same tool generates.
The Best Tech Deals From the Sam’s Club Early Black Friday Sale
We may earn a commission from links on this page. Deal pricing and availability subject to change after time of publication.
Retailers are churning out early Black Friday deals already, including the likes of Amazon, Best Buy, Walmart, and others. If you’re waiting around for Friday, Nov. 27 to do all of your shopping, you might miss out on some deals and unnecessarily make the day more stressful than it needs to be. If you’re a Sam’s Club member, you have access to many early Black Friday deals worth checking out. I spent some time combing through their website and rounded up my favorite tech deals below.
The 2nd Gen. Bose SoundLink Flex SE is $89 ($50 off)
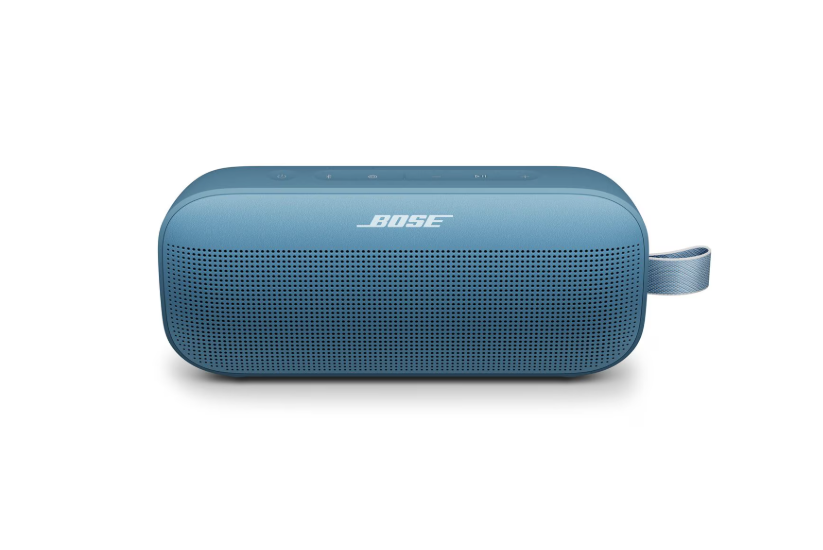
The Bose SoundLink Flex SE is a portable Bluetooth speaker with an IP67 waterproof rating. The speaker even floats in the water, so you can bring it with you into the pool. While it doesn’t offer full EQ customization in its companion app, the sound has rich bass depth and clear highs out of the box. It also features a speakerphone, allowing you to take calls and speak with it. It’s light and portable, and the Bluetooth 5.3 supports multipoint connectivity and SBC, AAC, and aptX codecs. You can get the Bose 2nd Generation SoundLink Flex SE for $89 (originally $139).
The Skullcandy Stomp XL Max is $99 ($100 off)
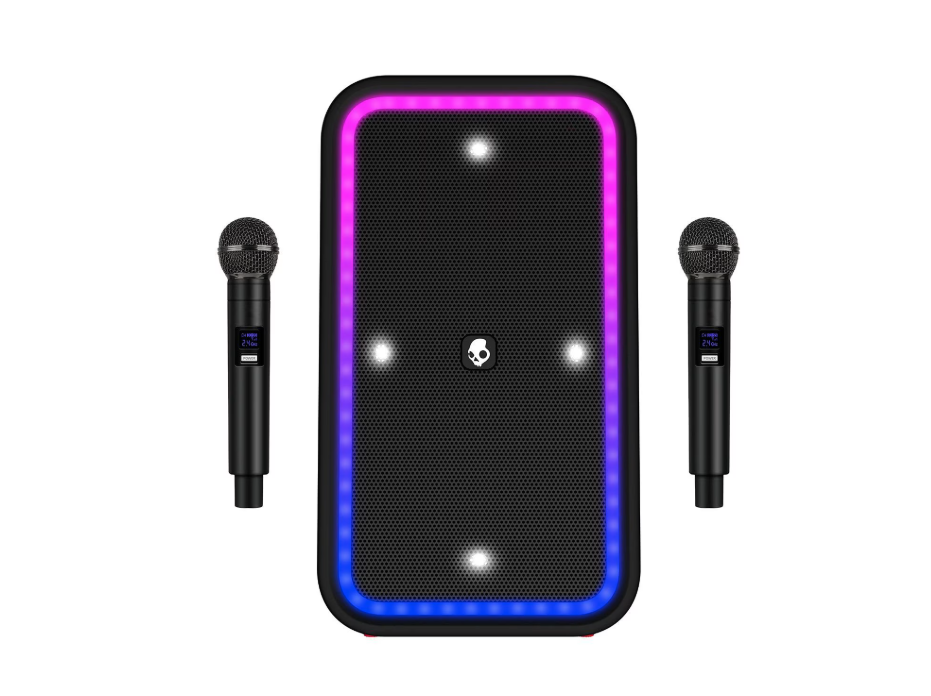
Skullcandy makes fun speakers and headphones, although they’re not designed for audiophiles (their sound signature is very bass-heavy). Their Skullcandy Stomp XL Max is their attempt at making a portable party speaker. It comes with two wireless mics, making it a great option for karaoke. It holds 12 hours of battery life (up to 20 hours with certain settings), has an IPX5 water resistance rating, and has LED lights that sync to the music. You can get it for $99 (originally $199).
The Samsung HW-Q65F 5.1 Channel Soundbar is $299 ($100 off)
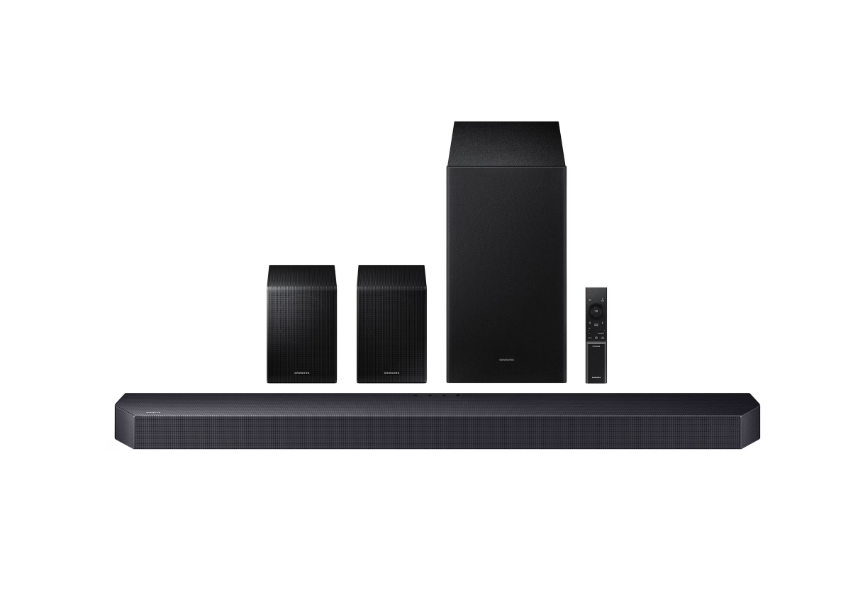
Getting a soundbar can exponentially improve anyone’s entertainment system, but a 5.1 system with rear speakers and a subwoofer takes it to the next level. The Samsung HW-Q65F 5.1 Channel Soundbar is $299 (originally $399), and it’s a wireless setup that will keep the harmony of “too many cables” in the house. It supports Dolby Atmos and DTS Virtual:X to give you a 3D audio feel, and it has a dialogue feature that will let you hear the whispers.
The 31.5-inch MSi Gaming Monitor is $129 ($50 off)
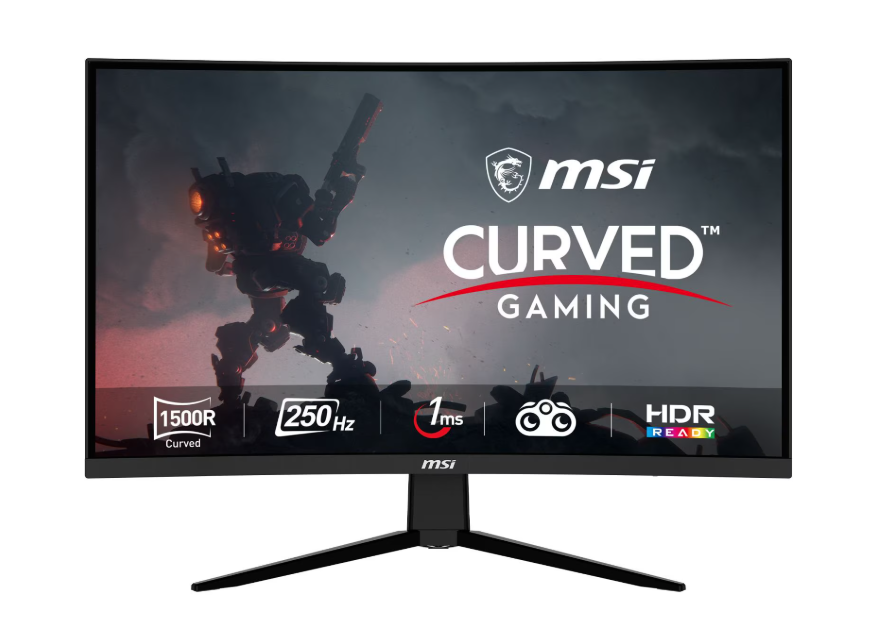
Gaming monitors can get expensive quickly, but you can get decent options on a budget. A great example is the 31.5-inch MSi gaming monitor selling for $129 (originally $179). It has a 250Hz refresh rate and a 1ms response time to make gaming smoother. There’s also AMD FreeSync Premium to get rid of tearing and stuttering.
The HP OmniBook 7 Flip laptop is $699 ($200 off)
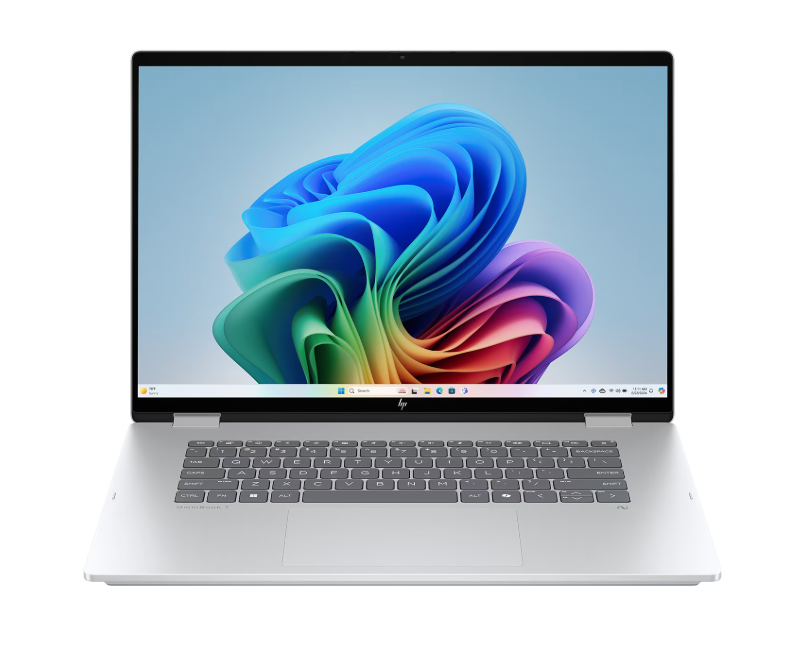
These kinds of sales are always a good time to upgrade laptops. If you’re looking for a powerful computer that is well-rounded, consider the 16-inch HP OmniBook 7 Flip going for $699 (originally $899). This laptop comes with an Intel Ultra 5 processor, 512GB of SSD, and 16GB of RAM (which, honestly, is the minimum anyone should be buying in 2026).
The HP OmniBook 3 laptop is $649 ($350 off)
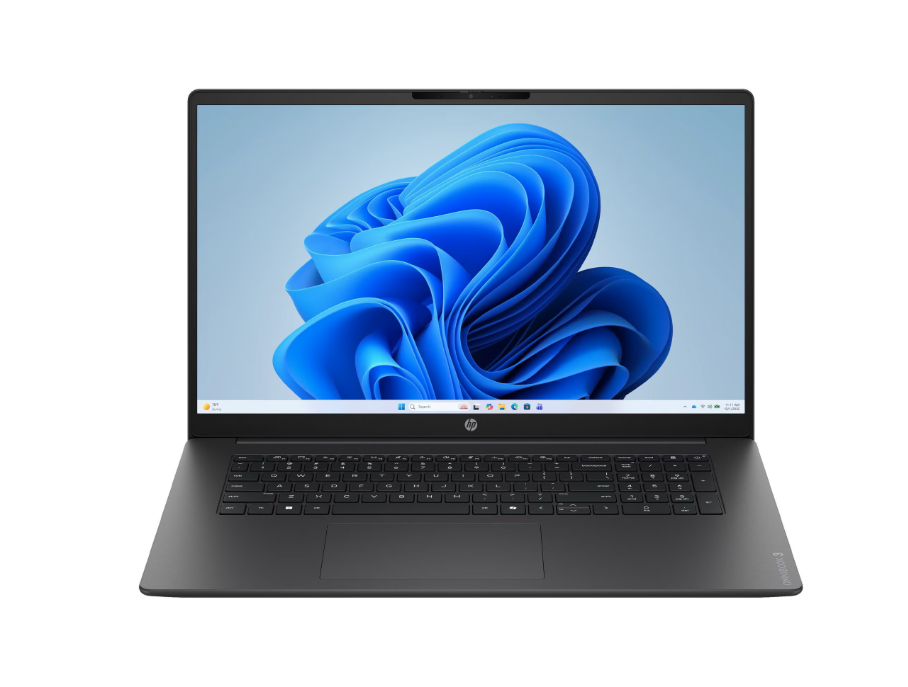
If you need a bigger screen, the 17.3-inch HP OmniBook 3 is a good choice for a bit less money. It comes with an Intel Core Ultra 7 processor, 512GB of SSD, and 12GB of RAM. Part of the bigger screen means a bigger keyboard, so if you deal with numbers a lot, you’d likely appreciate the numeric pad.
The ASUS TUF F16 Gaming Laptop is $1,149 ($150 off)
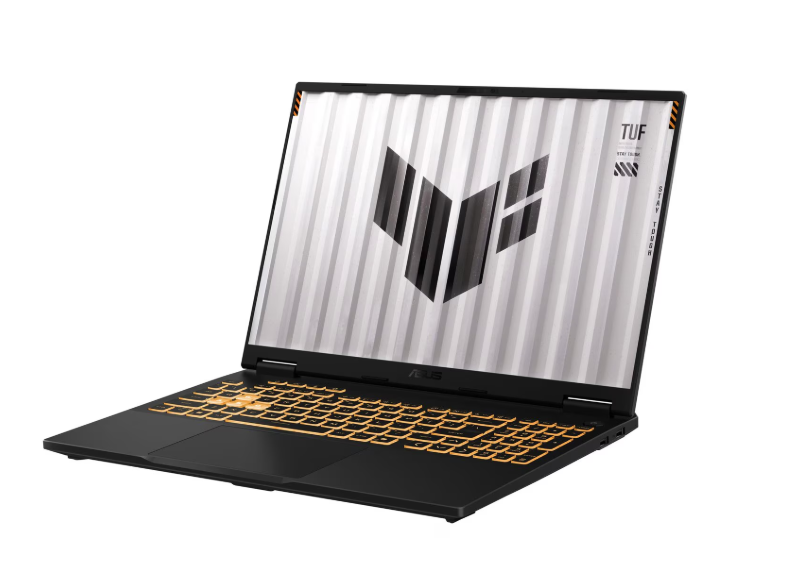
If you want your laptop strictly for gaming, the ASUS TUF F16 Gaming laptop is $1,149 (originally $1,399). With an Intel Core 7 processor and the RTX 5060 graphics card, you’ll be well set up to tackle heavy games. It comes with a 165Hz refresh rate, Advanced Arc Flow fans and vents to keep your machine cool, and 16GB DDR5 RAM to keep your loads short.
The 58-inch Vizio QLED TV is just $178 ($120 off)
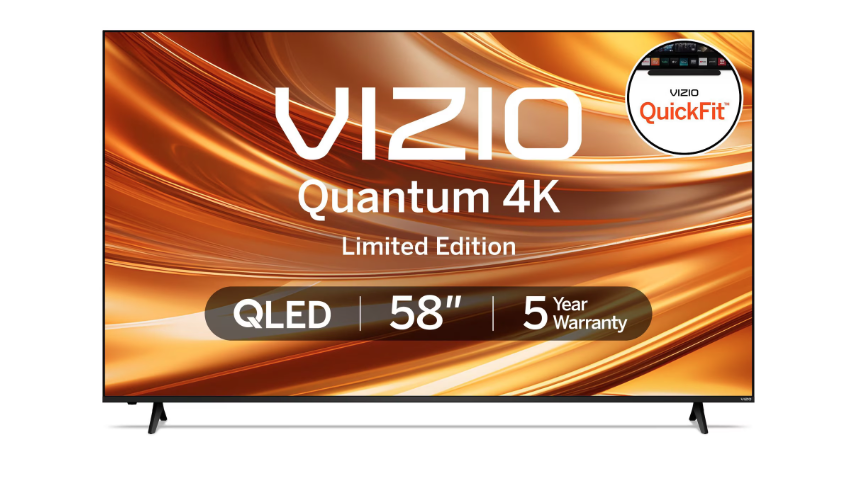
Budget TVs get big discounts during Black Friday, and the 58-inch Vizio QLED TV is one of them. You can get one for $178 (originally $298), and it supports Dolby Vision HDR for better color and contrast. The operating system is the Vizio OS, but of course, you can always change it with a TV dongle if you prefer a different one.
The Samsung QN90H QLED TV is $1,197.99 ($300 off)
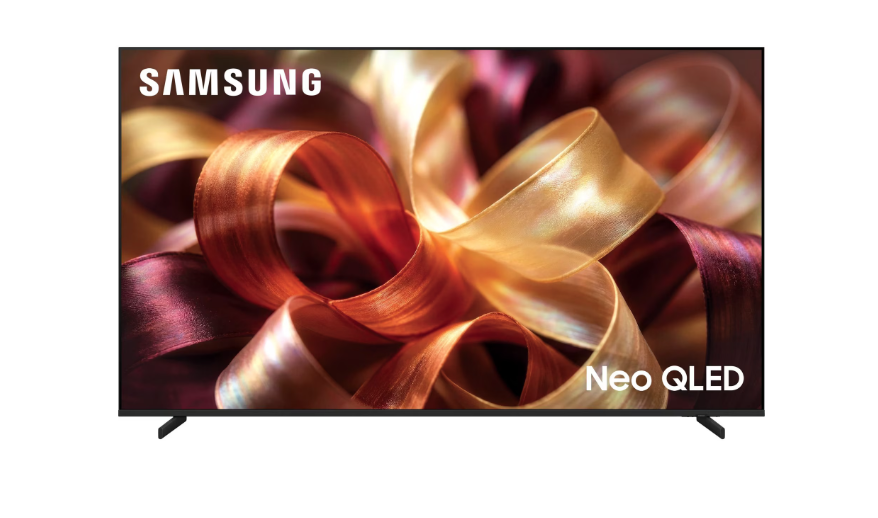
If you prefer to splurge for a better QLED but still get a good deal, the 65-inch Samsung QN90H QLED TV at $1,197.99 (originally $1,497.99) is a great option. It upscales lower-resolution pictures to 4K with AI. It works for gaming with its 144Hz refresh rate, and because the operating system is Tizen OS, it comes with Samsung TV Plus, which brings over 2,700 free channels. The TV also comes with Dolby Atmos, so you can hear audio with a 3D effect as the audio follows objects around the display.
The 100-inch Vizio QLED TV is $1,198 ($300 off)
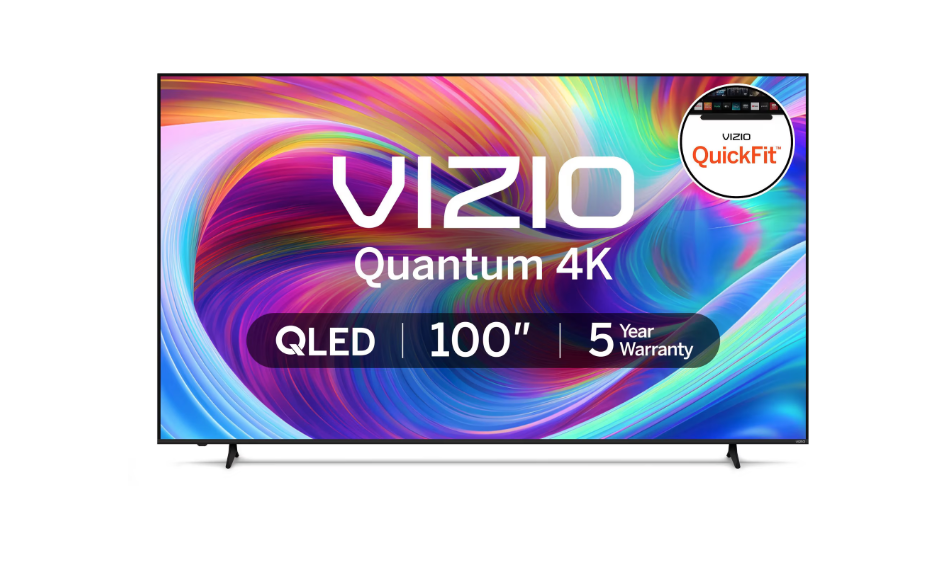
A 100-inch TV makes a statement: You take your entertainment system seriously. The 100-inch Vizio QLED TV is a budget-friendly option with a $300 discount, currently going for $1,198 (originally $1,498). This TV supports Dolby Vision HDR for more vivid images and has hundreds of free channels with the Vizio OS.
Black Friday FAQs
What stores have the best sales on Black Friday?
Nowadays, both large retailers and small businesses compete for Black Friday shoppers, so you can expect practically every store to run sales through Monday, November 30, 2026. The “best” sales depend on your needs, but in general, the biggest discounts tend to come from larger retailers who can afford lower prices: think places like Amazon, Walmart, Target, Best Buy, and Home Depot. You can find all the best sales from major retailers on our Black Friday coverage.
How long do Black Friday deals really last?
Black Friday sales officially begin Friday, November 27, 2026, and run throughout “Cyber Week,” the five-day period that runs from Thanksgiving through Cyber Monday, November 30, 2026. But Black Friday and Cyber Monday dates have expanded as retailers compete for customers. You can get the same Black Friday sales early, and we expect sales to wind down by December 2, 2026.
Are Black Friday deals worth it?
In short, yes, Black Friday still offers discounts that can be rare throughout the rest of the year. If there’s something you want to buy, or you’re shopping for gifts, it’s a good time to look for discounts on what you need, especially tech sales, home improvement supplies, and fitness tech. Of course, if you need to save money, the best way to save is not to buy anything.
Our Best Editor-Vetted Early Black Friday Deals Right Now
Deals are selected by our commerce team
‘Ghost Accounts’ Are Putting Your Security at Risk, but You Can Protect Yourself
In all the years you’ve been online, you’ve likely created more accounts than you can remember, whether to shop on a website you made one purchase from, sign up for a newsletter you’ve since stopped reading, or download apps for school or work that you no longer need.
These so-called “ghost accounts”—all the old, forgotten logins that are still active but not in use—could expose your data in the event of a breach, increasing the risk of your information being used in malicious ways. That’s why it’s important to go through the effort to find and delete dormant accounts. Here’s how to get started.
How old accounts can compromise your security
As McAfee describes, ghost accounts may retain lots of sensitive data, such as your contact details (phone numbers, emails, and addresses), purchase histories, payment details, and passwords. While this doesn’t mean your information is sure to be compromised, the more places it lives, the more opportunities there are for bad actors to get ahold of it.
You’re less likely to be keeping tabs on activity in older accounts, which may also have weak or reused passwords that haven’t been updated in years. If that company or service experiences a data breach, not only is your stored data there exposed, but that information (including your password) can be used to access other accounts using tactics like credential stuffing and phishing. This also increases the risk of identity theft, as threat actors can use your name, birth date, and other information to open fraudulent accounts.
How to find and delete your old accounts
Unfortunately, finding and removing forgotten accounts can be tedious. If you have a password manager, the easiest way to start is to audit older items as well as look at security reports that identify weak or reused passwords, as well as data breaches that have impacted your accounts. If you’ve saved credentials in your browser keychain, go through the same process to find dormant accounts.
The next place to look is in your email: Search for account confirmation and verification emails as well as password resets using keywords like “verify your email,” “free trial,” “welcome,” “confirm your account,” or “sign up.” Add a date filter to narrow down older accounts. Do this across all of your email addresses.
Next, audit accounts you’ve created using single sign-on, such as Google, Apple, or Facebook. For Google, this is under Account Settings > Linked apps. For Apple, go to System Settings > [Your Name] > Sign in with Apple on your Mac (or the same path in the Settings app on iOS). On Facebook, this is under Settings & privacy > Apps and websites. Disconnecting these accounts won’t automatically delete them, but you can add them to the list to take action. Finally, you can search your email(s) on HaveIBeenPwned and username(s) on IDCrawl or WhatsMyName to find dormant accounts.
Once you’ve found accounts you no longer use, the next step is to deactivate or delete them, which you may be able to do through the settings or by reaching out to customer support. At the very least, remove all identifying information and change the password, and if possible, update the address to a burner using your browser’s or password manager’s hide-my-email feature. If you no longer have access to an old account, that doesn’t mean it’s been deactivated and your information removed, so you may need to reach out to customer support to find out how to access and delete it.
Highly Classified NSA Network Goes Down
“CNN and other outlets are reporting that a classified network at the NSA is down,” writes longtime Slashdot reader frdmfghtr. “This follows a week of major outages at Microsoft, the FAA, and JPMorgan Chase.” From a report: The network, called NSANet, allows employees to communicate classified information internally. At this point there is no evidence of a cyberattack, sources said. As the agency works to understand the scope of the problem, it has enacted staggered arrivals for personnel, the sources said.


“We see no evidence that this was a cyberattack,” White House spokesperson Lauren Bis said Tuesday on Newsmax. “There is no crisis, or anything like that, for Americans to be worried about.” […] The US shares intelligence with a group of countries in what is known as the Five Eyes intelligence-sharing alliance, which includes the US, UK, New Zealand, Australia and Canada. That intelligence sharing system has not been impacted as a result of the NSANet outage, according to a source from one of the countries and a former US intelligence official. The NSA released a statement addressing the network issues: “The National Security Agency experienced temporary degradation during scheduled routine maintenance. While some internal systems were affected, mission-critical capabilities remain fully operational and our ability to defend national security continues. NSA’s infrastructure is designed with multiple layers of redundancy to maintain operations during planned maintenance or unexpected events.”
Read more of this story at Slashdot.
Civilization studio Firaxis Games lays off a third of staff
Firaxis Games, the studio behind the Civilization and XCOM franchises of computer strategy games, last week laid off about a third of its staff, totaling around 60 people. That’s according to a recent report in Bloomberg.
The report cites people “familiar with the cuts,” saying that the flagship game the studio is currently working on, a new entry in the XCOM series, “has faced development struggles and missed a significant milestone.” The departures also include the studio head, Heather Hazen.